It’s 11:00 PM on the Friday before a long weekend. The streets are quiet, and your office is dark. Most of your team is asleep. But in a highly automated, windowless room halfway across the world, a software script is wide awake—and it just found an open door in your company’s network.
When we talk to business owners across the Midwest, we hear a common refrain: “I run a local business in Missouri. Hackers are in Russia or North Korea. Why would they care about my small operation?”
It’s a logical question. But it’s also the exact mindset cybercriminals are banking on.
Today’s cyber threats aren’t a guy in a hoodie furiously typing on a keyboard, manually picking targets. They are highly sophisticated, automated operations that scan millions of internet connections every hour, looking for the easiest path inside. To these automated scripts, you aren’t a local construction firm, accounting practice, or healthcare clinic. You are simply an IP address with a vulnerability.
If you’ve ever wondered what cybersecurity actually means for your daily operations, why standard antivirus isn’t cutting it anymore, or what you should actually be expecting from your IT provider, you are in the right place.
The Wake-Up Call: Busting the Two Biggest Cybersecurity Myths
Before we can build a strong defense, we have to tear down the two most dangerous misconceptions holding small and mid-sized businesses (SMBs) back.
Myth 1: “We’re too small to be a target.”
Many business owners assume they fly under the radar. The reality? You are the sweet spot. Attackers view SMBs as the ultimate low-hanging fruit. You have enough cash flow to pay a ransom, but you likely don’t have an enterprise-level IT security budget or a dedicated team monitoring your network at 2 AM.
Myth 2: “We don’t have any valuable data.”
You might think, “We don’t store credit cards or classified secrets. What is there to steal?”
Hackers don’t just want your data to sell it; they want leverage and access.
- Leverage: They know you can’t run your business, run payroll, or serve your customers if you are locked out of your own files. The ransom isn’t for the data’s open-market value; it’s the price of your business continuity.
- Access: Attackers frequently use small businesses as stepping stones. If they can hijack your email, they can send malicious invoices to your larger vendors, partners, or clients, using your hard-earned trust as a weapon.
Anatomy of an Attack: The Phishing-to-Ransomware Pipeline
If you look up cybersecurity advice on government websites, you’ll see warnings about “Phishing” and “Ransomware” treated as two separate problems. This leaves many people confused about how attacks actually happen.
Think of it like this: Phishing is the stolen key, and Ransomware is the changed locks.
Here is how a modern attack typically unfolds:
- The Phishing Lure: An employee gets an email that looks exactly like a Microsoft 365 password reset or a shared document from a trusted vendor.
- The Stolen Key: They click the link and type in their password. They don’t realize they just handed their login credentials to a hacker.
- The Silent Wait: The attacker logs in, but they don’t strike immediately. They sit quietly, sometimes for weeks, reading emails, learning who handles finances, and finding where the backups are stored.
- The Ransomware Payload: Usually on a Friday night or a holiday—when they know your IT guy is offline—they unleash the ransomware. This malicious software rapidly scrambles (encrypts) every file, server, and backup it can touch, effectively changing the locks on your entire business.
Jargon Translator: The Physical Security Analogy
Technology is full of confusing acronyms. Let’s translate the most important ones into plain English:
- Endpoint: Think of these as the doors and windows of your business (laptops, phones, servers).
- Lateral Movement: When a hacker breaks into one window (an employee’s laptop) and sneaks through the hallways to find the vault (your main server).
- SOC (Security Operations Center): The 24/7 team of armed security guards monitoring your cameras and doors, ready to tackle an intruder the second they step foot inside.
Why the “Old Way” of IT Security is Failing
Ten years ago, buying a good antivirus program and setting up a firewall was enough. Today, that approach is dead.
Basic antivirus relies on “signatures.” It has a list of known bad viruses, like a bouncer with a physical list of banned people. If a virus isn’t on the list, the bouncer lets it right in. Because hackers create thousands of new, unique variations of ransomware every single day, standard antivirus software is functionally blind to modern attacks.
Furthermore, traditional IT support is built for standard business hours. If an attack launches at midnight on a Saturday, a standard break-fix IT provider won’t even realize you’ve been breached until Monday morning at 8:00 AM. By then, the damage is completely irreversible.
The Modern Defense Architecture: How to Actually Stop an Attack
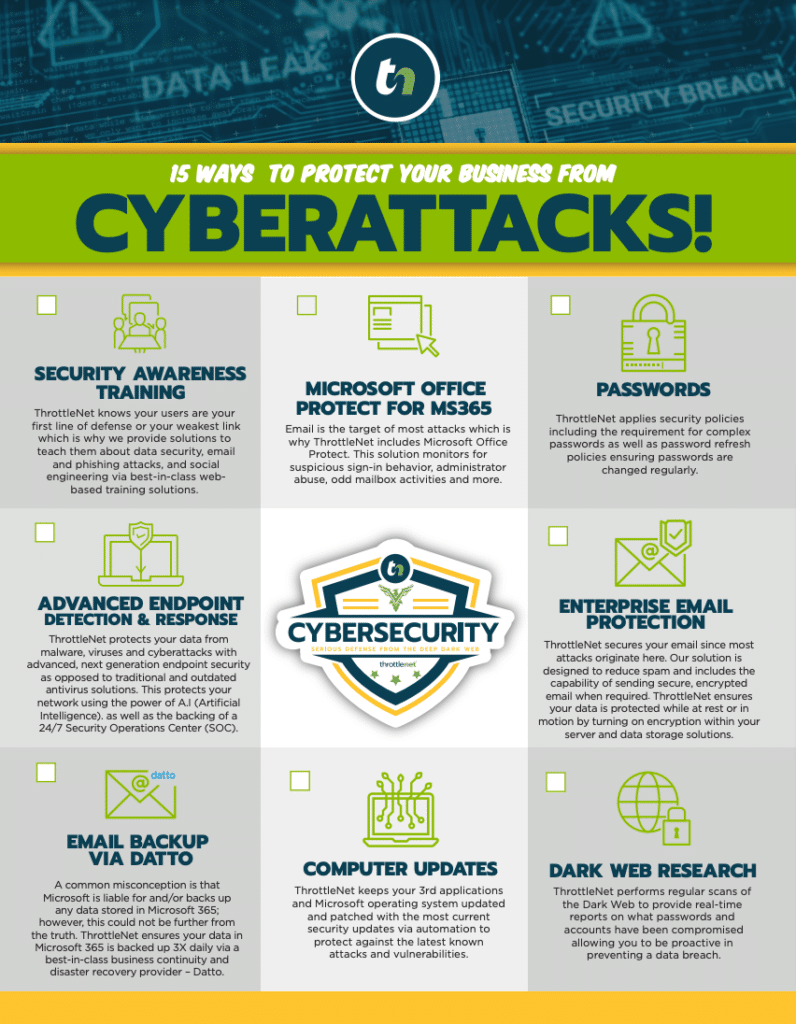
To protect your business today, you need to shift from passive software to active, continuous defense. Here is what a modern, enterprise-grade architecture looks like, scaled for SMBs:
1. Next-Generation Endpoint Protection
Unlike old antivirus software, next-gen endpoint protection doesn’t just look for known bad files; it looks for bad behavior. If Microsoft Word suddenly tries to delete your entire hard drive, the next-gen software recognizes that this is abnormal behavior and instantly kills the process before the files can be scrambled.
2. A 24/7 Security Operations Center (SOC)
Technology alone isn’t enough; you need human experts watching the alerts. A 24/7 SOC acts as your persistent threat monitor.
Let’s look at an Attack Timeline with a SOC in place:
- Minute 1: An employee accidentally clicks a sophisticated phishing link on a Sunday afternoon.
- Minute 3: A malicious script attempts to run in the background.
- Minute 4: Next-gen endpoint protection flags the anomaly and alerts the SOC.
- Minute 5: Human security engineers at the SOC isolate the infected laptop from the rest of the network.
- Minute 8: The threat is neutralized. Your business didn’t suffer a minute of downtime, and the infection never reached your servers.
3. Real Financial Accountability
In the IT industry, talk is cheap. Many managed service providers (MSPs) will sell you a stack of security software, but if you get breached, you’re the one left holding the bag. A true cybersecurity partner should have skin in the game.
This is where financial guarantees change the landscape. For example, ThrottleNet backs its cybersecurity solutions with a $500,000 cybersecurity protection program. Why? Because accountability matters. If a vendor trusts their security stack, their SOC, and their team, they should put their money where their mouth is. (It’s also why ThrottleNet customers have never paid a ransomware attack).
4. Unprecedented Speed
When a user is locked out of an account, or a suspicious email comes through, you can’t afford to wait. The industry average for an IT support response can stretch into hours or even days. In contrast, an elite support infrastructure is built for speed, routing issues directly to the right level of expertise. ThrottleNet, for example, delivers an industry-leading average response time of just 90 seconds, paired with a 93% same-day resolution rate. Fast response isn’t just a convenience; it is a critical component of security.
Your Role-Based Cybersecurity Checklist
Creating a culture of security doesn’t mean you have to become an IT expert. It means knowing what you are responsible for. Use this CISA-inspired framework to delegate your defense:
For the Business Owner / CEO
- [ ] Demand a Strategy, Not Just Software: Ensure your IT provider acts as a Virtual Chief Information Officer (vCIO), providing quarterly strategic reviews and budgeting, not just a help-desk phone number.
- [ ] Verify Financial Protections: Check your cyber liability insurance policies and ask your IT vendor if they offer any financial protection guarantees.
- [ ] Establish a Culture of Verification: Create a company-wide rule that any wire transfer or invoice change must be verified by a phone call, completely separate from email.
For the Office Manager / Operations Lead
- [ ] Enforce MFA Everywhere: Ensure Multi-Factor Authentication (MFA) is turned on for all email, payroll, and banking applications.
- [ ] Streamline Off-boarding: Have a strict, same-day checklist for disabling access when an employee leaves the company.
- [ ] Champion User Training: Schedule regular, bite-sized training sessions (often provided by your IT partner) so the team knows how to spot the latest phishing trends.
What Your IT Provider MUST Handle
- [ ] 24/7 SOC Monitoring: Ensure human eyes are on your network after hours and on weekends.
- [ ] Verified Backups: They shouldn’t just run backups; they should routinely test restoring them to prove they work.
- [ ] Next-Gen Security: Confirm they are using behavioral-based endpoint protection, not legacy signature-based antivirus.
- [ ] Speed of Resolution: Demand metrics. If they can’t prove a response time measured in seconds or minutes, you are exposed.
Frequently Asked Questions About SMB Cybersecurity
What happens if one of my employees clicks a bad link? If you only have basic antivirus, the malicious software will likely deploy and spread through your network. If you have next-gen endpoint protection backed by a SOC, the software will isolate the compromised machine, and a security team will intervene before the infection can spread.
Is moving to the cloud (like Microsoft 365) enough to keep me safe? No. While Microsoft secures the physical servers, you are responsible for securing your accounts, data, and access. If a hacker gets your Microsoft password, they simply log in through the front door. You still need advanced email protection, MFA, and independent cloud backups.
Can I just use my local “IT guy” for cybersecurity? While a solo IT professional might be great for fixing printers or setting up new computers, true cybersecurity requires a multi-tiered team. One person cannot monitor your network 24/7/365, stay updated on the latest global threat intelligence, and provide strategic business planning all at once.
Securing Your Business for the Future
The shift from reactive “break-fix” IT to proactive, managed cybersecurity is one of the most important transitions a growing business will make. The threats targeting organizations are sophisticated, relentless, and fully automated.
But with the right architecture—a 24/7 SOC, next-generation endpoint protection, expert vCIO guidance, and lightning-fast support—you can neutralize these threats before they ever impact your bottom line.
You built your business through hard work and local trust. Don’t let an automated script running at midnight take that away. Education is the first step; taking proactive control of your IT environment is the next.